Hacked website cleanup: what the process looks like from first call to final report
When a site is hacked, the owner faces two problems at once. The first is technical: the site redirects visitors, sends spam or shows someone else's content. The second is practical: they don't know who to turn to, what that person will do, how long it will take, or how to know the job is really done.
This article answers the second problem. We describe what hacked website cleanup looks like with us, step by step: what happens after your first call, what we need from you, what we do on the site, how you know it's finished and what you get at the end. No secrets and no jargon.
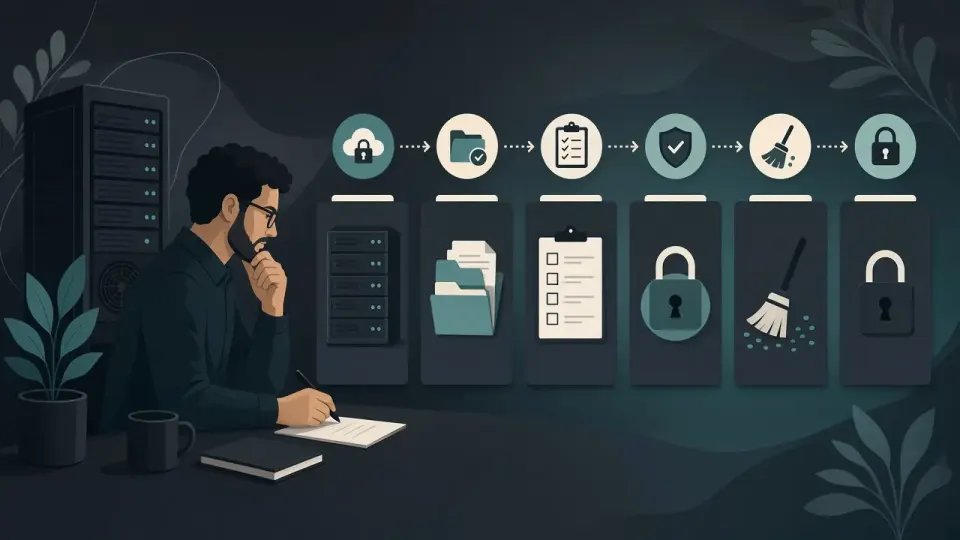
In short: hacked website cleanup has six phases: intake and quick assessment, a safe copy, a deep review of files and database, removal of malware and backdoors, closing the entry point, and a control check with a report. Prices start from €100, urgent cases from €150. We confirm the exact amount before any work begins.
Request a cleanup → or call +381 65 402 5000
Why the process matters more than speed
Under pressure, many site owners look for someone to "just get rid of it quickly". That's understandable: the site isn't working right, clients are asking, Google shows a warning. But a cleanup done fast instead of thoroughly almost always ends with the same phone call a week or two later.
The reason is simple. What you see, a redirect, spam pages or injected code, is only the consequence. The cause is the entrance the attacker used and, almost always, a spare entrance they left for themselves. If only the visible part is removed, the attacker comes back through the same door and injects the code again. We covered this in detail in infection returns after cleanup.
That's why our process isn't "find it and delete it", but a sequence of steps where each one has a clear goal and a clear limit.
Phase 1: Intake and quick assessment
Everything starts with your message or call. To begin, we only need a few things:
- the site address,
- a short description of what's happening: what you see, since when, who noticed,
- if you received an email from your host or Google, forward it, because it often contains useful information about the cause,
- whether the site is currently online or your host has suspended the account.
The first thing we do is a quick remote assessment. We run the same check you can run yourself on the free website check page: a review of public content, redirects and Google Safe Browsing status. In a few minutes that gives us a first picture: what's visible from outside and how urgent it is.
Based on that, you get an answer: what you probably have, what we suggest as the next step and an approximate price. Nothing is done on the site before you agree.
How we decide urgency
Not every case is equally urgent. The highest priority goes to:
- sites whose host has suspended them, because they don't work at all,
- sites with a red warning in Chrome, because they turn away every visitor,
- shops, because every hour of downtime means lost sales,
- sites sending spam, because every hour damages the domain's reputation.
For those cases there's the Emergency Response package, from €150, handled ahead of regular requests during the business day. For sites that are infected but can wait in the regular queue, there's Standard Incident, from €100.
Phase 2: Access and a safe copy

Deep work needs access to the site. With us that usually means installing a dedicated tool on the site, which sees files, the database and accounts and sends findings to our monitoring panel. If the site is down or there's no admin access, we work through hosting access.
Before any change we make a full copy of the files and database, including the infected parts. It's a rule with no exceptions, for two reasons:
- If something during cleanup goes differently than expected, there's always a way back.
- Infected files are evidence. They show when the infection started and how it got in, which is key to closing the entrance.
Panic-deleting suspicious files without a copy is the most common mistake owners make when they try to do it themselves. Why that's risky, we explain in DIY malware removal vs professional.
Changing passwords
As soon as we have access, all key passwords are changed: WordPress admin, database, hosting panel and FTP. If the attacker got in with a stolen password, this closes their easiest way back while the rest of the work is done.
Phase 3: Deep review of files and database
This is the heart of the whole process. The goal isn't just to find what's visible, but to find everything that shouldn't be there.
The review covers:
WordPress core. Core files are compared with the official version. Any difference is suspicious, because a legitimate site doesn't modify core files.
Themes and plugins. We check whether theme and plugin files differ from the originals, whether there are plugins nobody installed, and whether outdated versions with known vulnerabilities are present.
The uploads folder. This folder should hold images and documents. A PHP file in it is almost always a backdoor.
mu-plugins and drop-ins. WordPress loads them automatically and doesn't list them with regular plugins. A favorite hiding place.
The database. Options, page and post content, users and scheduled tasks are reviewed. Some infections live only in the database.
Users. We look for administrator accounts nobody on your side created, as well as accounts whose privileges were raised later.
Scheduled tasks (cron). Attackers leave tasks that re-inject code a few days later. This is one of the main reasons infections come back.
.htaccess and server rules. Redirects are often injected straight into server rules, where an owner would never look.
If you'd like the details of how a backdoor search works, we describe it in how to find a WordPress backdoor.
Phase 4: Removing malware and spare entrances
Only when the picture is complete does removal begin. The order matters:
- Spare entrances are removed first: backdoor files, fake administrators, malicious scheduled tasks. This goes first so the attacker can't react while the rest of the cleanup is under way.
- Visible malware is removed: injected code in the theme, database and server rules, redirect scripts or spam-sending scripts.
- Core files are replaced with a clean official version.
- Modified plugins and themes are replaced with clean versions from official sources, keeping your settings.
At every step we make sure the site keeps working. The goal of cleanup isn't an empty site without malware, but your site, with your content and settings, without malware.
Phase 5: Closing the entry point

This step is the difference between a cleanup that lasts and one that repeats. Once everything is removed, the path the attacker used is closed:
- updating core, themes and plugins,
- removing unused themes and plugins,
- replacing plugins that are no longer supported,
- blocking PHP execution in the uploads folder,
- invalidating all active sessions and changing security keys, so the attacker is kicked out even if they stole a login cookie,
- checking file and folder permissions.
If the cause was something specific, such as a pirated (nulled) theme or a vulnerable contact form, it's called out in the report with a suggestion for what to replace.
Phase 6: Control check and report
When the work is done, both the remote check and the deep review are run again to confirm nothing is left. With the Emergency Response package there's also a control check a few days later, to see whether the signal has returned.
At the end you get a short report with:
- what was found and where,
- what was removed,
- what the most likely entry point was,
- what was closed,
- what we recommend next.
The report isn't a formality. If your host asks what you did before reactivating the account, or a client asks what happened, you have a concrete answer.
The most common entry points we find

Every case is different, but the entry points repeat. Knowing the most common ones makes it clear why the closing phase matters so much.
Outdated plugins. By far the most common cause. A plugin not updated in years has a publicly known vulnerability, and automated scripts scan the internet every day looking for exactly those sites. The attacker doesn't care whose site it is; they care that it runs that plugin version.
Pirated (nulled) themes and plugins. A paid theme downloaded for free from an unofficial site very often comes with a backdoor built in. The site is compromised from day one; nobody has noticed yet.
Stolen or weak passwords. A password reused in several places leaks from some other service and is automatically tried on your site. Or the admin password is so simple it gets guessed.
Another site on the same hosting account. If you keep several sites on one account, an infection on a forgotten old site easily spreads to the main one. The owner cleans the main site, and the source stays on the other.
Vulnerable contact forms and old scripts. Hand-coded forms or old PHP scripts that aren't part of WordPress and were left on the server from earlier days.
Former collaborators with access. Less common, but it happens: the account of a former developer or agency that was never disabled, with a password that has since leaked.
In the report we always state the most likely entry point. Not for form's sake, but because it determines what needs to change so it doesn't happen again.
Example: what a typical case looks like
To make the process concrete, here's a typical case, described in general terms without client details.
A small business owner gets in touch because a client said the site sent them to a prize-draw page from their phone. When the owner opens the site on a computer, everything looks normal. The host hasn't been in touch, and Google shows no warning.
The remote check confirms the redirect: the site behaves differently for mobile visitors coming from search. The owner accepts the quote, we get access, make a copy and change the passwords.
The deep review finds injected code in one theme file that conditionally loads an external script. But it also finds what the owner couldn't have seen: two PHP files in the uploads folder, an administrator account with a name that looks like a system account, and a scheduled task that puts the code back into the theme every few days if someone deletes it. The entry point was a gallery plugin that hadn't been updated in three years.
Spare entrances are removed first, then the injected code, then core and theme files are replaced. The vulnerable plugin is replaced with a maintained alternative. The control check a few days later is clean.
If the owner had deleted only the code from the theme, which would be the natural first move, the scheduled task would have brought it back within days and the backdoor would have stayed open. That's exactly why the process goes in order rather than taking shortcuts.
After cleanup: Google, hosting and reputation
Cleanup solves the cause, but some consequences recover at their own pace.
Google warning. If the site was on Google's blacklist, a review request is submitted through Search Console after cleanup. Google responds within a few days. Details are in website blacklisted by Google.
Spam pages in the index. Pages the attacker created can stay in Google results even after cleanup. How they're removed is covered in remove spam pages from Google index.
Suspended hosting account. The host receives a description of what was found and removed, along with the report. A concrete description significantly speeds up reactivation.
Domain email reputation. If the site sent spam, email from your domain may land in spam folders for a while. Recovery is gradual.
How to know the cleanup is really finished
Owners rarely ask this, but they should. "The site looks normal now" isn't enough proof, because before cleanup it often looked normal to the owner too. Here's how to tell that a hacked website cleanup was done properly, no matter who did it:
- You received a written report of what was found, where and what was removed. If nobody can tell you what the problem was, nobody can tell you it's solved.
- The likely entry point is stated, along with what was done to close it. A cleanup with no answer to "how did they get in" is half a job.
- Passwords were changed for all accounts: WordPress, database, hosting, FTP. And sessions were invalidated.
- The remote check is clean, from a computer and a phone, and when arriving from Google search.
- The administrator list contains only people you know.
- The control check a few days later shows no returning signal.
- The host reactivated the account, if it was suspended, and hasn't sent another warning.
If any of these is missing, the job probably isn't fully done. That doesn't have to mean bad intent, but it's a good reason to ask.
How long does hacked website cleanup take
The honest answer: it depends on the scope. But here's a framework:
- Quick assessment: within the business day of your contact, with priority for urgent cases.
- The cleanup itself: for most small business sites, from a few hours to a day or two, depending on site size and how deep the infection goes.
- Recovery in Google: a few days to two weeks after the review request.
- Email reputation recovery: weeks, gradually.
The longest cases are those where the site was cleaned "quickly" several times, so the infection left multiple layers in the meantime.
How much does it cost

Prices are indicative and depend on the site's condition, the scope of findings and urgency:
| Package | Price | For whom |
|---|---|---|
| Standard Incident | from €100 | confirmed breach, the site can wait in the regular queue |
| Emergency Response | from €150 | the site must be back fast: priority during the business day, closing holes and a control check |
| Maintenance | from €30/month | after cleanup, so the risk doesn't quietly return |
We always confirm the exact amount after a short assessment, before work begins. More on what drives the price in the cost of cleaning a hacked site.
What you can do while you wait
If you've contacted us and are waiting for a reply, here are a few things that help and can't hurt:
- Don't delete files that look suspicious. They're evidence.
- Don't restore an old backup blindly. It may be infected too.
- Don't switch hosts in a panic. Moving the site moves the problem.
- Write down what you noticed and when.
- Change passwords for hosting and WordPress, if you can log in.
- Keep all emails from your host and Google.
When it makes sense to do it yourself
Not every case needs a professional, and we say that openly. If you have technical experience, a clean backup you know predates the infection, and the site isn't a shop, cleaning it yourself can be a reasonable decision. An honest comparison of pros and risks is in DIY malware removal vs professional.
Help makes sense when:
- you don't know where the infection got in,
- the infection came back after the first cleanup,
- your host suspended the account,
- the site is a shop or brings in revenue,
- you simply don't want to spend time on work someone else does every day.
Get in touch and you'll get a clear plan
You don't need to know exactly what's wrong with the site. Just send us the address and a short description. You'll get an assessment, a suggested next step and a price before anything starts.
Request a cleanup → · +381 65 402 5000 · or start with a free website check